Mythos Leaked Day One — Via Vendor Environment, Not Anthropic Core
Bloomberg: unauthorized users reached Anthropic’s Mythos Preview on announcement day through a third-party vendor path tied to contractor Mercor’s breach plus endpoint guessing. Anthropic is investigating; says no evidence of impact on its own systems. The trade: ‘too dangerous for broad release’ still fails at the supply-chain edge.

Corrected October 14, 2026: Clarified that the incident account is Bloomberg's report, relayed by TechCrunch and Fortune with Anthropic's statement.
Gating a cyber-capable model to ~40 partners does not gate the vendor graph. The Bloomberg story’s non-obvious frame: Mythos’s day-one leak path was partner/contractor infrastructure and guessable endpoints, not a reported breach of Anthropic’s core production plane.
Bloomberg (April 21) reported a small unauthorized group accessed Mythos Preview — Anthropic’s restricted cybersecurity-focused model under Project Glasswing — on limited-release announcement day (~April 7–8 public window). Path: third-party vendor environment linked to contractor Mercor (prior breach tied to LiteLLM reporting), plus internet sleuthing (guessing API endpoints from Anthropic naming patterns) and private-forum coordination (Discord channels hunting unreleased access cited in coverage). One participant reportedly an employee of a third-party working with Anthropic.
Anthropic spokesperson: investigating unauthorized access to Claude Mythos Preview through a third-party vendor environment; no evidence the activity impacted Anthropic’s systems. No broader compromise or exfiltration reported in the cited coverage.
Intended gate vs what happened#
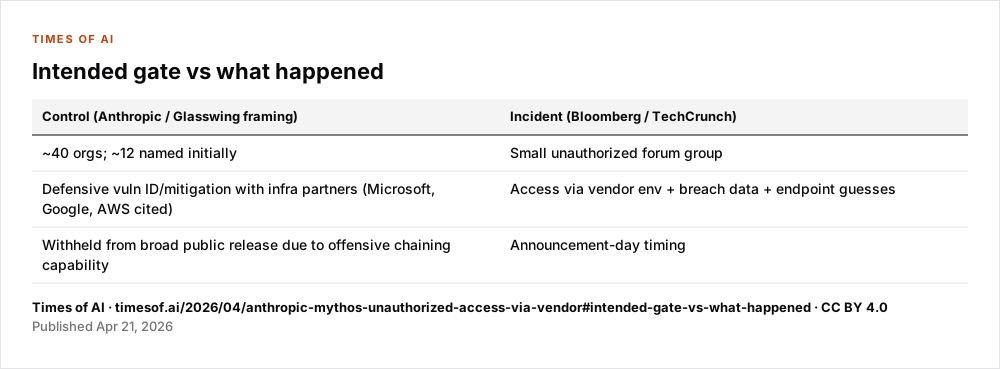
| Control (Anthropic / Glasswing framing) | Incident (Bloomberg / TechCrunch) |
|---|---|
| ~40 orgs; ~12 named initially | Small unauthorized forum group |
| Defensive vuln ID/mitigation with infra partners (Microsoft, Google, AWS cited) | Access via vendor env + breach data + endpoint guesses |
| Withheld from broad public release due to offensive chaining capability | Announcement-day timing |
Mythos’s demonstrated exploit-chaining across OSes/browsers (including old unpatched bugs) is Anthropic’s own capability framing for why access was narrow — not an independent red-team report.
Claims vs checks#
Incident narrative is Bloomberg's report, relayed by TechCrunch and Fortune with Anthropic's statement. Anthropic confirmation of investigation and “no evidence of impact” is company statement. Mercor/LiteLLM breach linkage and Discord hunting culture are reporter-sourced; treat method details as alleged pending fuller forensic disclosure.
Limits#
- Scope of what unauthorized users actually ran on Mythos is thinly reported.
- “No impact on Anthropic systems” does not equal “no useful capability extraction.”
- Full partner list and vendor security baselines remain private.
Sources#
- Bloomberg: “Anthropic’s Mythos Model Is Being Accessed by Unauthorized Users” (April 21, 2026).
- TechCrunch: unauthorized group access to Mythos (April 21, 2026).
- Cross-referenced coverage on Mercor, breach details, forum methods, Anthropic response.
- Fortune: A group of users leaked Anthropic’s AI model Mythos by reportedly guessing where it was located (April 23, 2026)
- Anthropic: Project Glasswing
- TechCrunch: Unauthorized group has gained access to Anthropic’s exclusive cyber tool Mythos, report claims (April 21, 2026)