Project Glasswing: Mythos Preview for Defenders — Gated, Credited, Partnered
Anthropic’s Project Glasswing channels Claude Mythos Preview — claimed thousands of high-severity vulns across major OSes/browsers — to ~12 named partners plus 40+ orgs, with up to $100M usage credits and $4M OSS security donations. Lab cyber benches beat Opus 4.6; independent public red-team replication is not the release.

The dual-use problem is no longer theoretical. Glasswing’s frame: give defenders Mythos-class vuln finding first, under partnership gates — because Anthropic says the model already beats most humans at finding and exploiting software flaws.
Anthropic (April 7) announced Project Glasswing and published Frontier Red Team assessments of Claude Mythos Preview. Founding partners named: AWS, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorgan Chase, Linux Foundation, Microsoft, NVIDIA, Palo Alto Networks. Access also to 40+ additional critical-software orgs. Commitments: up to $100 million Mythos Preview usage credits; $4 million to OSS security ($2.5M Alpha-Omega/OpenSSF via Linux Foundation; $1.5M Apache Software Foundation). Goal: defender head start before similar capabilities spread.
Capability claims (Anthropic)#
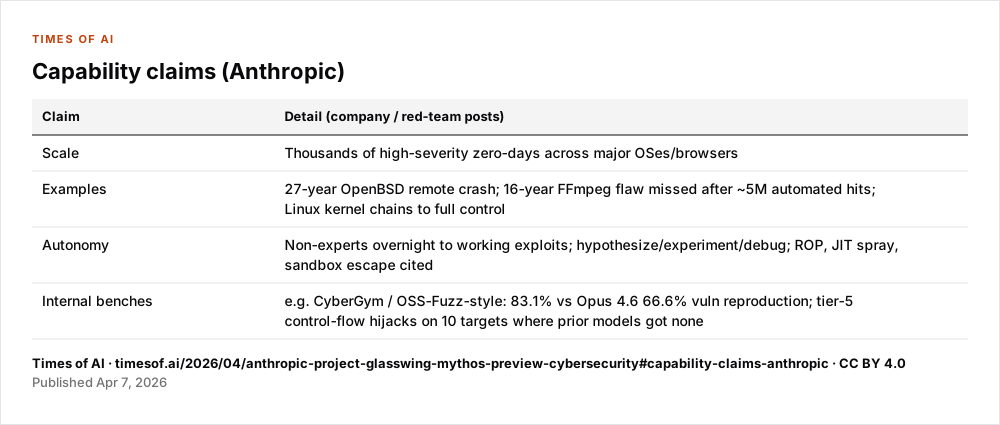
| Claim | Detail (company / red-team posts) |
|---|---|
| Scale | Thousands of high-severity zero-days across major OSes/browsers |
| Examples | 27-year OpenBSD remote crash; 16-year FFmpeg flaw missed after ~5M automated hits; Linux kernel chains to full control |
| Autonomy | Non-experts overnight to working exploits; hypothesize/experiment/debug; ROP, JIT spray, sandbox escape cited |
| Internal benches | e.g. CyberGym / OSS-Fuzz-style: 83.1% vs Opus 4.6 66.6% vuln reproduction; tier-5 control-flow hijacks on 10 targets where prior models got none |
Capabilities framed as emerging from general code reasoning/autonomy, not hacking-specific training.
Claims vs checks#
Partnership list, credits, and donations are Anthropic primary. Vuln counts and exploit anecdotes are lab red-team reporting — extraordinary claims without a public independent corpus dump. Later unauthorized-access reporting (April 21) shows gatekeeping is imperfect at the vendor edge — separate story, relevant risk context.
Limits#
- Mythos Preview not broadly released; public cannot verify.
- “Surpass all but the most skilled humans” is Anthropic rhetoric.
- Defender head-start assumes adversaries lack peer capability — unverifiable assumption.
- Credit utilization and fix rates unpublished at announcement.
Sources#
- Anthropic: “Project Glasswing: Securing critical software for the AI era” (April 7, 2026).
- Anthropic Frontier Red Team: “Assessing Claude Mythos Preview’s cybersecurity capabilities” (April 7, 2026).
- Partner announcements (Cisco, AWS, Microsoft, Linux Foundation) cross-referenced.