Daybreak Red’s 95% Is a Refusal Metric — CVE-2026-15903 Is the Check
OpenAI split Daybreak into Blue and Red and launched GPT-5.6-Cyber on Sol, claiming 95% completion on an internal advanced dual-use cyber eval versus 1.5% for Sol. OpenAI also reports a Chrome V8 CVE chain (CVE-2026-15903) — not the refusal board alone. Trusted-access cyber, not a ChatGPT default.

Frontier labs are racing to arm defenders without flooding the open internet with Critical-class cyber agents. Daybreak Red’s 95% “completion” figure is a refusal metric, not a guarantee of exploit quality — OpenAI’s reported Chrome CVE adds a concrete disclosure claim, not an independently checked result.
OpenAI published “Expanding Daybreak as the Cyber Defense Window Narrows,” splitting trusted cyber access into Daybreak Blue and Daybreak Red and launching GPT-5.6-Cyber — a cybersecurity-specialized model built on GPT-5.6 Sol. Blue unlocks Sol with defensive-security-calibrated safeguards; Red adds purpose-trained cyber models for authorized vulnerability research and exploit validation. On an internal Advanced Cybersecurity Completion Rate eval, GPT-5.6-Cyber completes 95.0% of advanced dual-use cyber requests versus 1.5% for Sol and 57.3% for GPT-5.5-Cyber. OpenAI says the model helped find two previously unknown V8 issues chained toward heap-sandbox escape, disclosed to Google and fixed as CVE-2026-15903.
What shipped#
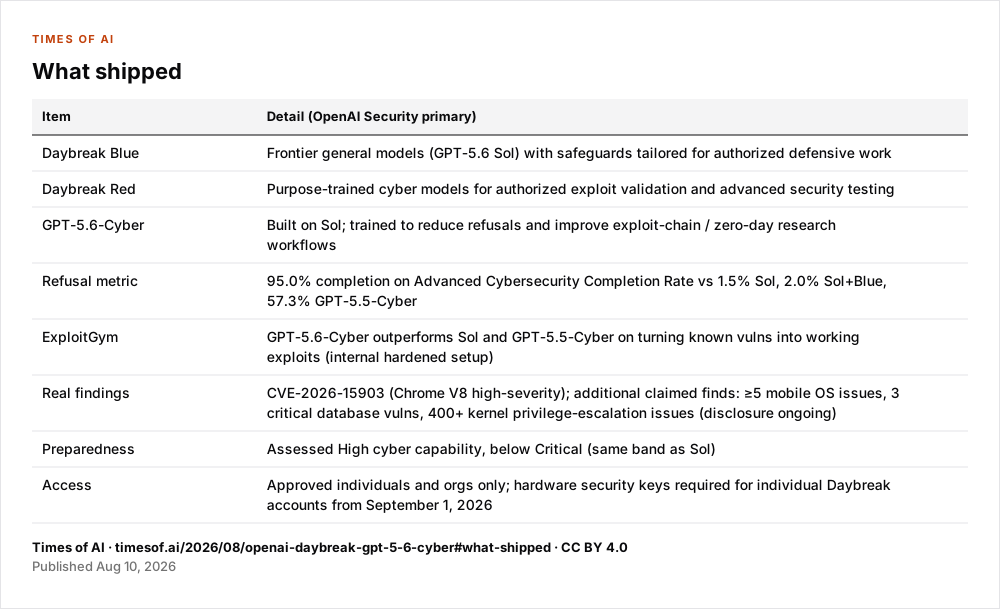
| Item | Detail (OpenAI Security primary) |
|---|---|
| Daybreak Blue | Frontier general models (GPT-5.6 Sol) with safeguards tailored for authorized defensive work |
| Daybreak Red | Purpose-trained cyber models for authorized exploit validation and advanced security testing |
| GPT-5.6-Cyber | Built on Sol; trained to reduce refusals and improve exploit-chain / zero-day research workflows |
| Refusal metric | 95.0% completion on Advanced Cybersecurity Completion Rate vs 1.5% Sol, 2.0% Sol+Blue, 57.3% GPT-5.5-Cyber |
| ExploitGym | GPT-5.6-Cyber outperforms Sol and GPT-5.5-Cyber on turning known vulns into working exploits (internal hardened setup) |
| Real findings | CVE-2026-15903 (Chrome V8 high-severity); additional claimed finds: ≥5 mobile OS issues, 3 critical database vulns, 400+ kernel privilege-escalation issues (disclosure ongoing) |
| Preparedness | Assessed High cyber capability, below Critical (same band as Sol) |
| Access | Approved individuals and orgs only; hardware security keys required for individual Daybreak accounts from September 1, 2026 |
OpenAI states GPT-5.6-Cyber was not involved in the earlier Hugging Face evaluation incident and is not an unrestricted public cyber free-for-all. Daybreak is trusted-access cyber distribution under identity gates.
Limits#
- 95% is completion/refusal, not independent exploit-quality scoring.
- Additional mobile/database/kernel find counts are lab-claimed with disclosure ongoing.
- System card and Blue vs Red enrollment scale not fully public here.
Correction and source review — October 14, 2026: Removed later distribution and unrelated Astra comparisons that were not supported by this launch source. Attributed the Chrome CVE finding to OpenAI; this review did not independently inspect Google’s vulnerability record.
Sources#
- OpenAI: Expanding Daybreak as the Cyber Defense Window Narrows (August 10, 2026)
- OpenAI Daybreak program
- CNBC: OpenAI expands Daybreak cybersecurity initiative (August 10, 2026)
- Times of AI:
openai-astra-critical-cyber-capabilities-pause(August 7)